About this resource
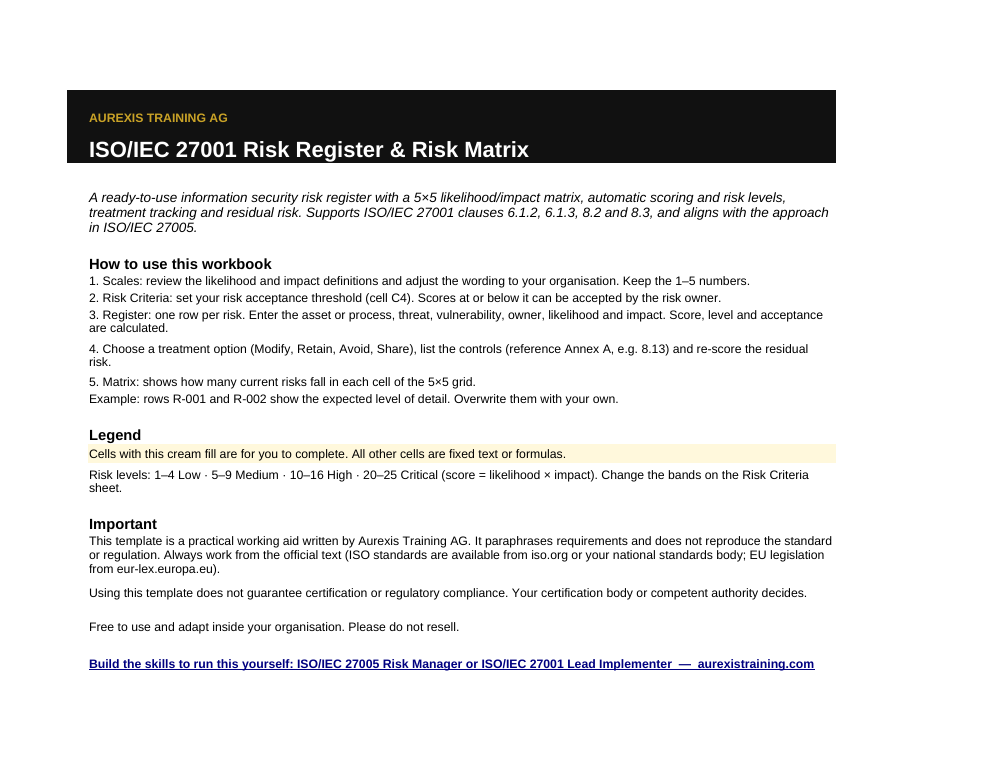
A working Excel risk register for ISO/IEC 27001 clauses 6.1.2, 6.1.3, 8.2 and 8.3. Adapt the likelihood and impact scales, set your acceptance threshold, record treatment decisions and re-score residual risk. The matrix and summary update from the register.
What’s inside
- 60 risk-register rows with two worked examples
- 5×5 inherent-risk matrix and residual-risk summary
- Editable likelihood, impact and acceptance criteria
- Treatment, control, owner, due-date and status fields
Download
- Get the Excel workbook (XLSX)
Related course: ISO/IEC 27005 Risk Manager
Frequently asked questions
How does the risk scoring work?
The workbook multiplies likelihood and impact on 1–5 scales. It then assigns Low, Medium, High or Critical levels using editable thresholds and checks the result against your acceptance criterion.
Can I track risk treatment and residual risk?
Yes. Record Modify, Retain, Avoid or Share, reference the selected controls, assign an action owner and due date, then enter residual likelihood and impact for an updated risk level.
Is this an official ISO or regulatory document?
No. It is a practical Aurexis working aid written in our own words. Always use the official standard or legislation for the authoritative requirements. Using a template does not guarantee certification or compliance.