About this resource
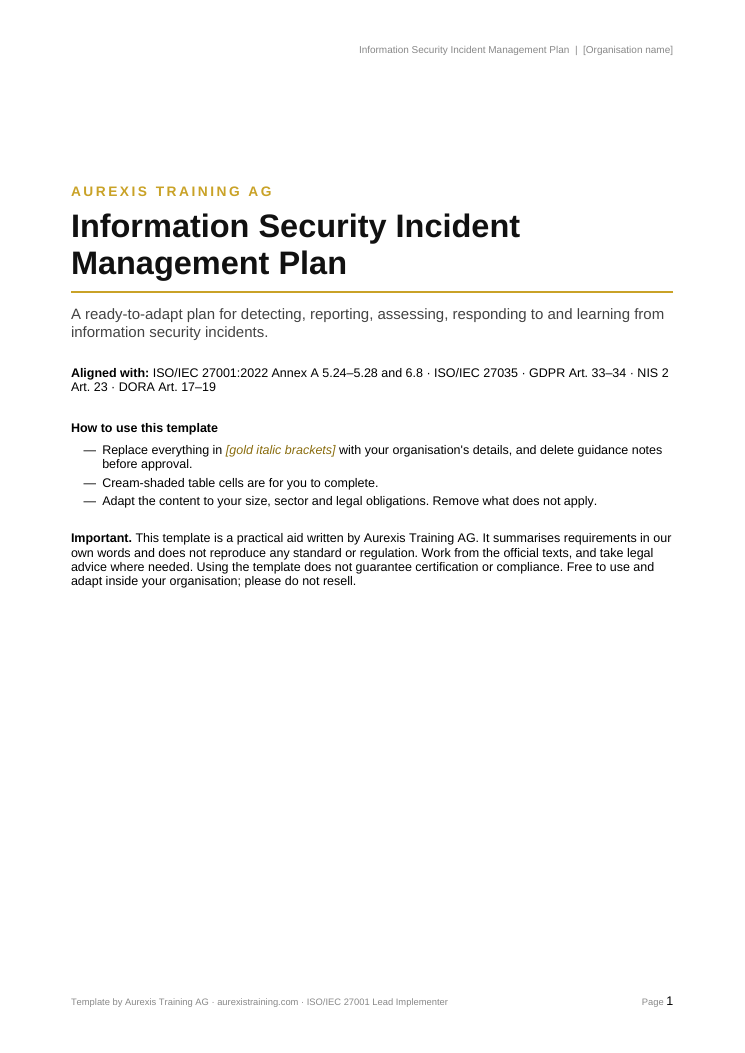
A seven-page editable Word template aligned with ISO/IEC 27001 incident controls and ISO/IEC 27035, with notification prompts for GDPR, NIS 2 and DORA. It includes document control, practical lifecycle guidance and appendices your team can use during exercises and real incidents.
What’s inside
- Seven editable Word pages
- Severity levels and end-to-end incident lifecycle
- GDPR, NIS 2, DORA and contractual notification prompts
- Report form, incident log, contacts, review and four quick playbooks
Download
- Download Word template (DOCX)
Related course: Lead Cybersecurity Manager
Frequently asked questions
What should I customise first?
Replace the bracketed guidance with your organisation's roles, contacts, severity criteria, response targets and applicable notification duties. Delete guidance notes before approval and remove regimes that do not apply.
Are incident playbooks included?
Yes. Quick playbooks cover ransomware, phishing and account compromise, lost or stolen devices, and data sent to the wrong recipient.
Is this an official ISO or regulatory document?
No. It is a practical Aurexis working aid written in our own words. Always use the official standard or legislation for the authoritative requirements. Using a template does not guarantee certification or compliance.